

Independent verification of code quality
To build enterprise-grade codebases, an independent and objective certification layer for code quality is essential. Using the same tool to generate and verify code will result in poor code quality.
Unified trust layer
It acts as an independent verification and assurance layer for all code, whether AI-generated or human-written (first-party and open source). This prevents any type of defect from entering the codebase, protecting against risks introduced by new coding assistants.
Consistent deterministic results
This is the central advantage of SonarQube over probabilistic code scanning tools that produce noisy, inconsistent results at each analysis.
Deterministic assurance
SonarQube is the only solution that guarantees consistency. Our analyzer will consistently find the exact same software bug given the same code. This reliability is vital for driving developer action and building trust in the tool vs. chasing intermittent fleeting issues.
Unmatched breadth, depth, and precision
SonarQube's analysis engine offers technical superiority that translates directly into reduced defects and higher efficiency.
Advanced detection
Uniquely capable of catching complex bugs hidden across multiple files that other tools miss.
Comprehensive breadth
Supports over 35 programming languages and frameworks, ensuring a unified code quality and security standard across your entire technology stack.
High precision
Our sophisticated analysis yields a significantly low false positive rate. Low noise prevents developer fatigue, allowing developers to focus only on fixing real code quality issues.
Enforceable automated governance
SonarQube establishes a clear, non-negotiable definition of quality that is enforced automatically throughout the developer workflow.
Quality gates as non-negotiables
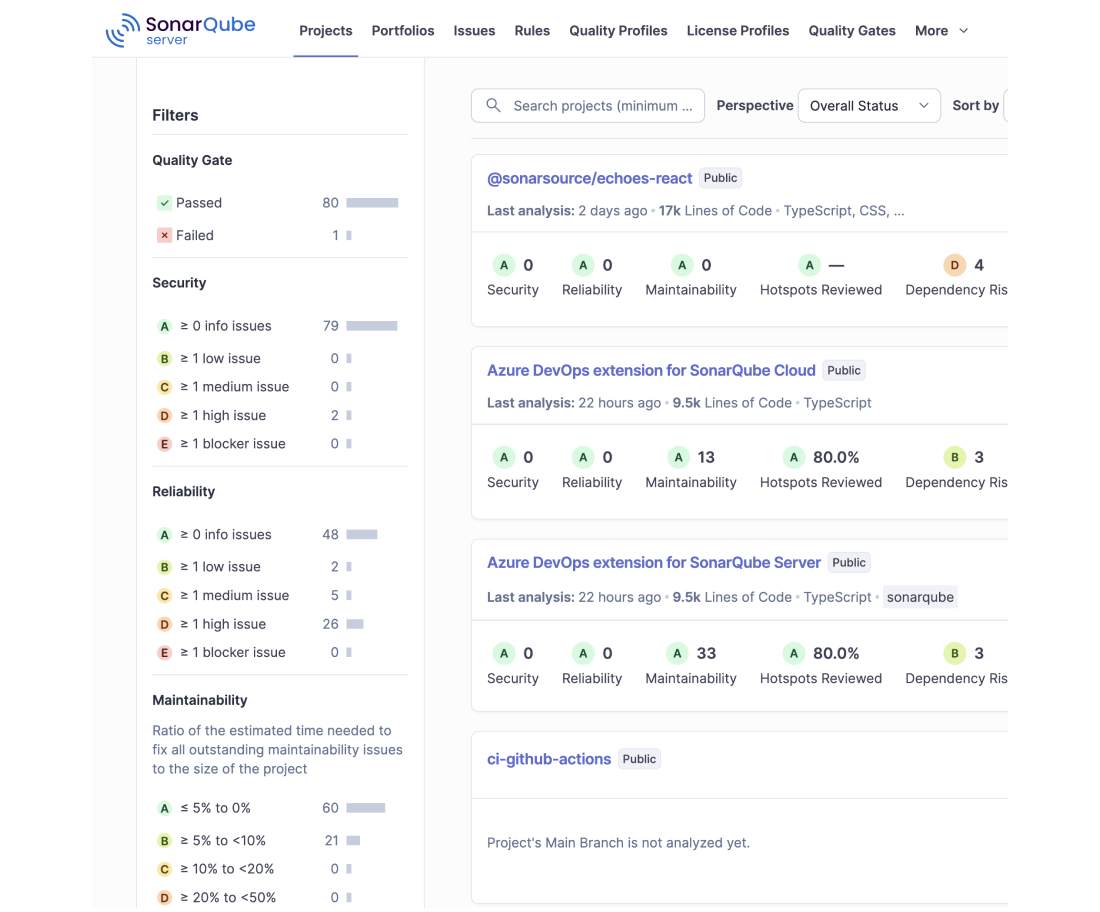
Quality gates codify your non-negotiable standards as automated "go/no-go" criteria enforced at every Pull Request. This ensures main only contains the highest quality code and can be deployed at any moment.
Context-aware and Shift-left validation
The analysis is smart, fast, and fully integrated, making quality part of the development lifecycle rather than a late stage roadblock.
Context-aware analysis
Analysis is deeply aware of the surrounding code, utilizing language, framework, and build-system–awareness. This includes deep dataflow, taint tracking, secrets detection, SAST, and cognitive complexity analysis.
True shift-left
Provides real-time feedback in IDEs and agents (SonarQube for IDE) to catch and fix issues instantly as developers write.